On 21 October 2026, two critical vulnerabilities affecting PHP were publicly disclosed, raising serious concerns for organisations running PHP-based websites and applications, including well-known CMS such as WordPress, Drupal and Joomla.
Somewhere out there is a subdomain nobody at your company remembers creating.
CVE-2025-55182 is a newly disclosed critical vulnerability (CVSS 10.0) affecting React Server Components (RSC), enabling attackers to execute arbitrary code on
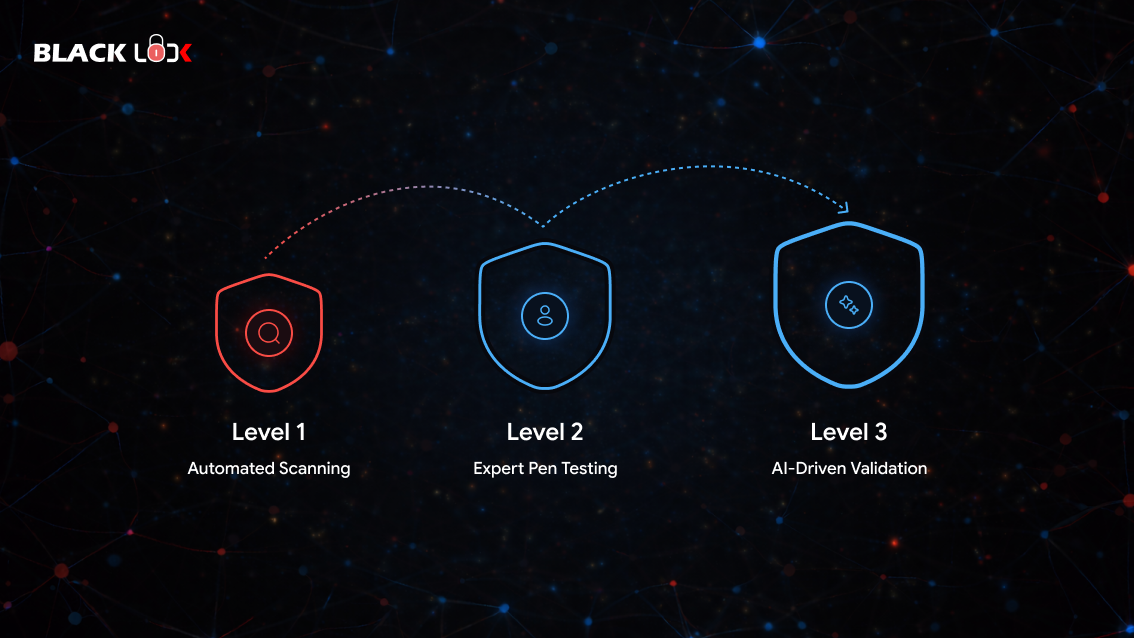
Most SaaS companies know they need a more mature secure development lifecycle. Fewer know how to get there without hiring a dedicated AppSec team or grinding through months of process change.
Think about what it actually takes to exploit a publicly accessible web application today. According to IBM's 2026 X-Force Threat Intelligence Index, attacks that begin with exploiting public-facing
A customer database is exposed. An attacker gains access to your web application. An employee discovers that personal information may have been downloaded without authorisation.
For nearly a decade, the Essential Eight has given Australian organisations a practical baseline for reducing common cyber risks. That baseline is now entering a transition period.
Earlier this year, Gartner introduced Continuous Offensive Security Testing, or COST, as a framework for rethinking how organisations approach offensive security validation.
Today, software is built and delivered faster than ever, but that speed has come with a cost. The integrity of the software supply chain is now one of the most actively targeted areas in cyber security.
